

Introduction
Nowadays, attackers’ knowledge and sophistication level is increasing steadily, making a single defensive method against intruders insufficient in providing substantial security. Instead, organizations should prioritize implementing a comprehensive and multi-layered strategy that combines proactive and defensive measures to safeguard their network and assets from unauthorized individuals. That’s where IDS, IPS, and firewalls come into action. But which security measure to choose? For that, one should know the basic difference between IDS and IPS.
In this blog, we will explain IDS and IPS in detail and also the difference between the two. Let’s Begin!
IDS vs IPS – What’s the Difference?
The main difference between IDS and IPS is how they respond to suspicious network activity. IDS detect possible threats and alert the security team, while IPS detects and blocks threats automatically. IDS is mainly used for monitoring and investigation, while IPS is used for real-time prevention and active network protection.
| Factor | IDS | IPS |
| Full Form | Intrusion Detection System | Intrusion Prevention System |
| Basic Definition | A security tool that monitors traffic and detects suspicious activity | A security tool that detects suspicious activity and blocks it in real time |
| Main Function | Detection and alerting | Detection and prevention |
| Working Mode | Passive security system | Active security system |
| Deployment Style | Usually deployed out-of-band using mirrored or copied traffic | Usually deployed inline, directly in the traffic path |
| Action After Detection | Sends alerts to the administrator or SOC team | Blocks, drops, resets, or rejects malicious traffic automatically |
| Traffic Control | Does not directly control live traffic | Directly controls live traffic before it reaches the target |
| Response Time | Depends on how quickly the security team reviews and acts on alerts | Immediate response because action is automated |
| Network Impact | Low impact because it only monitors copied traffic | Can affect performance because all traffic passes through it |
| Best Used For | Monitoring, investigation, compliance, and traffic visibility | Real-time threat prevention, critical networks, and public-facing systems |
| Example Use Case | Detecting unusual login attempts, malware activity, or suspicious internal traffic | Blocking malicious packets, exploit attempts, port scans, or known attack signatures |
| Best Placement | Behind a firewall, near core switches, or in monitoring zones | Inline between firewall and internal network, or before critical servers |
Now that you have an idea of IDS vs IPS, let’s understand what IDS and IPS really are in detail.
What is an Intrusion Detection System (IDS)?
An intrusion detection system tracks any suspicious behavior that might compromise network security. An IDS will notify the administrator of the issue, but it may not take any further action. Different forms of IDS use various detection strategies.
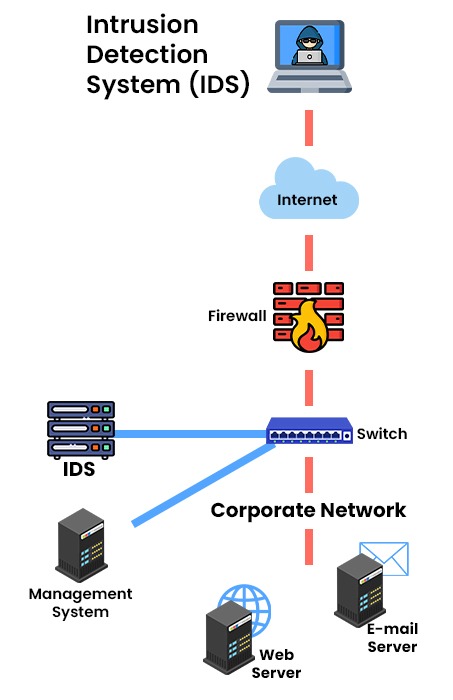
How IDS Works?
- Collecting network data or system logs.
- Analyzing the data using predefined rules and signatures.
- Identifies potential security threats.
- Sends alerts to administrators for further action.
Types of IDS
There are two types of IDS, namely HIDS and NIDS.
- Network intrusion detection system (NIDS): It is a kind of IDS that keeps tabs on data packets entering and leaving a network. All traffic or a subset of it might be monitored for risks. Potential threats are evaluated by an NIDS against patterns of hazardous activity. Due to its superior coverage compared to host-based systems, this is the favoured choice for large organizations.
- Host Intrusion Detection System (HIDS): A HIDS is a kind of IDS that is installed on and only watches over one host at a time (such as a computer). In addition to traffic, client behavior on the computer is also tracked. HIDS compares the host’s current checksum to a previously calculated one and notifies the system administrator if any difference is found.
Note: It is important to note that both NIDS and HIDS can work side by side. With HIDS and NIDS working together, sensitive devices or workstations will have further protection from potential threats. While malicious software may be able to bypass a NIDS, their activity will be detected by a HIDS.
Advantages of IDS
- Passive Monitoring: IDS gives you complete visibility into network activity without interfering with traffic. Potential attacks, policy infractions, and internal security breaches can all be found with its help.
- Identifies a Broad Spectrum of Attacks: Signature-based IDS can detect known attacks, while anomaly-based IDS can identify unusual activity, even for unknown threats.
Disadvantages of IDS
- No Active Response: IDS can only alert administrator about an attack. It is not capable of stopping or mitigating a potential attack.
- False Positives: IDS can also generate false positives where it considers a legitimate activity that might resemble an attack. It can overwhelm administrators with unnecessary notifications.
What is an Intrusion Prevention System (IPS)?
Intrusion prevention systems are considered as a subset of intrusion detection. Undoubtedly, the foundation of every intrusion prevention strategy lies in the first step of intrusion detection. However, security systems can take further measures and intervene in order to prevent current and potential future attacks. When an IPS identifies the presence of an attack, it has the capability to block incoming data packets, provide instructions to a firewall, and perhaps terminate a connection.
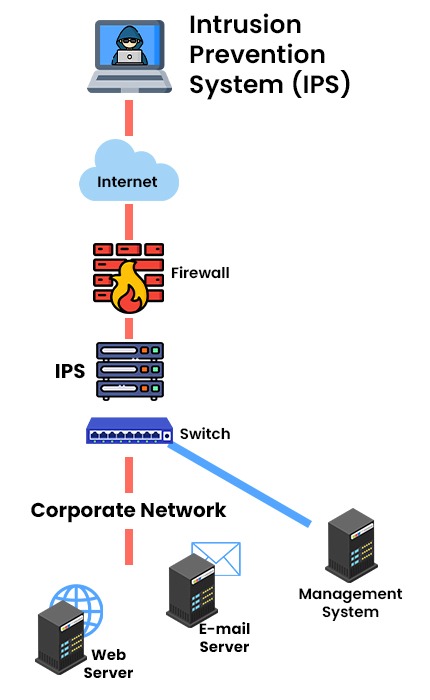
How IPS works?
- Monitors network traffic in real-time.
- Compares traffic with known attack signatures and behavioral patterns.
- Blocks malicious activities immediately.
- Logs the incident and alerts administrators.
Types of IPS
There are four types of IPS, namely NIPS, HIPS, WIPS, and NBA.
- Network-based Intrusion prevention system (NIPS): It is deployed at strategic points in the network, such as routers or firewalls, and analyzes all incoming and outgoing traffic.
- Host-based intrusion prevention system (HIPS): It is installed on individual hosts, such as servers or workstations, and monitors the system’s behavior and processes.
- Wireless intrusion prevention system (WIPS): It is designed to protect wireless networks from unauthorized access and attacks. In general, WIPS has two components, namely overlay monitoring and integrated monitoring.
- Network behavior analysis (NBA): It is a type of IPS that uses statistical analysis and machine learning to identify abnormal network patterns and anomalies. In simple words, It is similar to NIPS, but it works on anomalies.
Advantages of IPS
- Active Prevention: IPS can automatically block attacks in real-time, preventing malware or intruders from gaining access to the network.
- Reduces Damage: By stopping attacks as they happen, IPS can prevent damage, data breaches, or service disruptions.
- Integrated with Firewalls: Many modern firewalls have IPS capabilities built-in, providing an all-in-one solution for traffic filtering and intrusion prevention.
Disadvantages of IPS
- Consequences of False Positives: Because intrusion prevention systems operate automatically, false positives may result in the blocking of valid traffic, which could interfere with regular network traffic or company activities.
- Resource-intensive: Because IPS actively blocks traffic, it uses more resources than IDS. In situations with excessive traffic, this could result in latency if the system isn’t scaled appropriately.
Now we have a basic understanding of IDS and IPS, let’s discuss the difference between IDS and IPS in detail.
Difference between IDS and IPS
Here are the main difference between IDS and IPS:
1. Functionality:
IDS detects and alerts administrators to any suspicious activity. However, it is not capable of taking a direct action to stop that attack. On the other hand, IPS is capable of detecting and take immediate action against any suspicious attack. Thus, preventing the attack from continuing.
2. Deployment Mode:
IDS is deployed out-of-band. So, it is able to monitor the traffic without disrupting the network flow. It allows to monitor traffic passively. IPS is deployed in-line. It is directly in the flow of network traffic. It allows IPS to actively filter and block any malicious packet in real-time.
3. Response to threats:
IDS: It informs the administrator or security team about the potential attack. Then, team have to take manual action to investigate and mitigate the threat.
IPS: It automatically takes action by blocking malicious traffic, terminating connection, or applying patches.
4. Impact on Network Traffic:
IDS: It does not impact network traffic as it only observes and analyze the network traffic passively.
IPS: It can impact network traffic if it is not properly configured or overburdened. It can introduce latency in the network.
5. Complexity:
IDS: It is easier to deploy and manage.
IPS: It is more complex due to its in-line deployment and active blocking, requiring careful tuning and maintenance to avoid disruption.
Detection Methods Used by IDS and IPS
IDS and IPS tools use different detection methods to identify threats. The most common methods are:
Signature-based Detection
This method compares traffic with known attack patterns. It is useful for detecting known malware, exploits, port scans, and common attacks.
Anomaly-based Detection
This method compares current network activity with normal behavior. If the system finds unusual traffic volume, strange login patterns, or abnormal communication, it generates an alert or takes action.
Policy-based Detection
This method checks whether traffic violates predefined security policies. For example, if a user tries to access a restricted server or unauthorized application, the system can detect or block it.
Modern IDS and IPS solutions often use a combination of these methods to reduce false positives and improve threat detection accuracy.
Use Cases of IDS and IPS in Real Networks
Use Cases of Intrusion Detection System
Intrusion Detection System is useful for organizations that want visibility without affecting live traffic. It is often employed for monitoring traffic compliance reporting, log analysis, forensic investigation, and identifying suspicious activity in the network.
Use Cases of Intrusion Prevention System
Intrusion Prevention System is useful in situations where an organization requires immediate protection. It is typically installed near data centers, firewalls, as well as public-facing apps, cloud workloads, and crucial areas of networks where stopping threats swiftly is essential.
Combined Use Case of IDS and IPS
Many companies utilize IDS and IPS in conjunction. IDS provide detailed visibility and logs, whereas IPS offer immediate security. This layered approach can help security personnel to detect, investigate, and block threats more efficiently.
Now we have compared IDS vs IPS, but the question that arises now is which one is better? Let’s understand.
Which is better IDS or IPS?
The best is the one that best serves the company’s purposes. While it’s true that both IDS and IPS solutions have their strengths, IPS is considered a superior all-around cybersecurity option. The automatic characteristics of an IPS are luring many businesses away from IDS systems.
Since IDS solutions can only alert users during an attack, many businesses are switching to IPS to prevent further damage. The user is responsible for manually fixing the problem.
However, an IPS can detect and stop the assault while it is happening. Whenever a security event occurs, the user-defined automated actions and rules may be triggered immediately. If malicious data is being sent to your network from an outside source, the application may either block that IP address or reset the connection.
IPS systems have a significant advantage because of their ability to both detect intrusions and block them. When managing risks, an ISP’s automatic reactions are superior to manually remediating security events after getting an alert.
When to use IDS vs IPS?
Intrusion Detection System (IDS) is used when passive monitoring and visibility into network activity without impact on traffic. It is mainly used in networks where you need to analyze traffic, detect threats, and manually take action for that threat.
Intrusion Prevention System (IPS) is used for real-time threat prevention, mainly in high-security environments. It is used in environments where the network is exposed to frequent external threats, such as public-facing servers or web applications.
Can you combine IDS and IPS?
Yes, it is possible to combine IDS and IPS. In many security architectures, IDS and IPS are used together for comprehensive protection. The IDS can provide detailed logs and alerts, while the IPS takes real-time action to prevent attacks. This hybrid approach ensures both visibility and proactive defense, offering layered security for critical networks.
Frequently Asked Questions
Q1. What is the difference between IDS and IPS and firewall?
Firewalls assist in blocking as well as filtering network traffic, whereas IDS is only for the detection of intrusions, and IPS assists in blocking as well as alerting of intrusions.
Q2. Can IDS and IPS work together?
IDS and IPS are two types of network security systems that can work together to protect a network from malicious attacks. By combining IDS and IPS, a network can detect and prevent intrusions, enhancing its security posture.
Q3. What is IDS and IPS devices?
The intrusion detection system (IDS) is responsible for monitoring network traffic, analyzing the traffic to identify signatures that match known attacks, and promptly notifying the user in the event of any suspicious activity. Meanwhile, the traffic continues to flow. An intrusion prevention system (IPS) is responsible for the monitoring of network traffic as well as blocking the infected packets or the server from where the packet is transmitting.
Q4. Why are IDS and IPS needed?
IDS (Intrusion Detection System) and IPS (Intrusion Prevention System) are needed to monitor and protect network traffic from malicious attacks.
Conclusion
When assessing a security solution, it is important to consider that internet security threats are progressively becoming more discreet and harmful. Hence, it is advisable to have multi-layer security against such threats. In this blog, we have explained IDS and IPS in detail, as well as the basic difference between IDS and IPS.