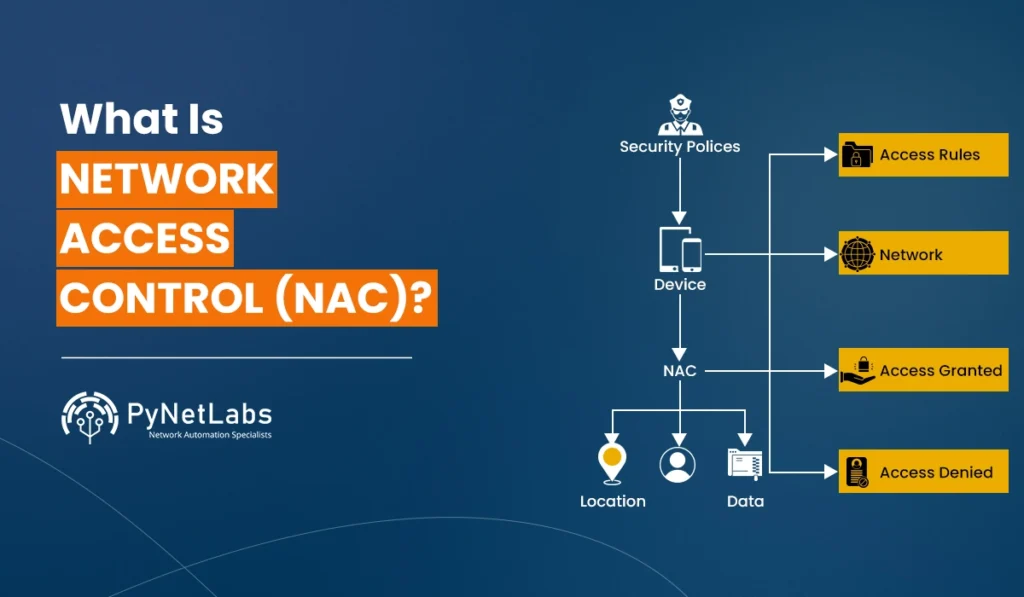
Network access control is a security measure that controls who and what can connect to a company network and then limits what each connection can reach. Modern NAC checks more than the password and username. It may assess the user, device type, safety postures, ownership, and more prior to giving access.
It is important because business networks are now managed laptops, personal devices, cameras, printers, phones, IoT equipment, contractors, and guests. A network access control provides IT teams a central location to monitor these connections and implement consistent rules. In this blog, we will discuss NAC in networking and how does it work along with use cases and real-world benefits.
Let’s start by first understanding what Network access control (NAC) is.
What Is Network Access Control?
Network access control, or NAC, works like a real-time policy checkpoint between a connection request and the resources behind it.
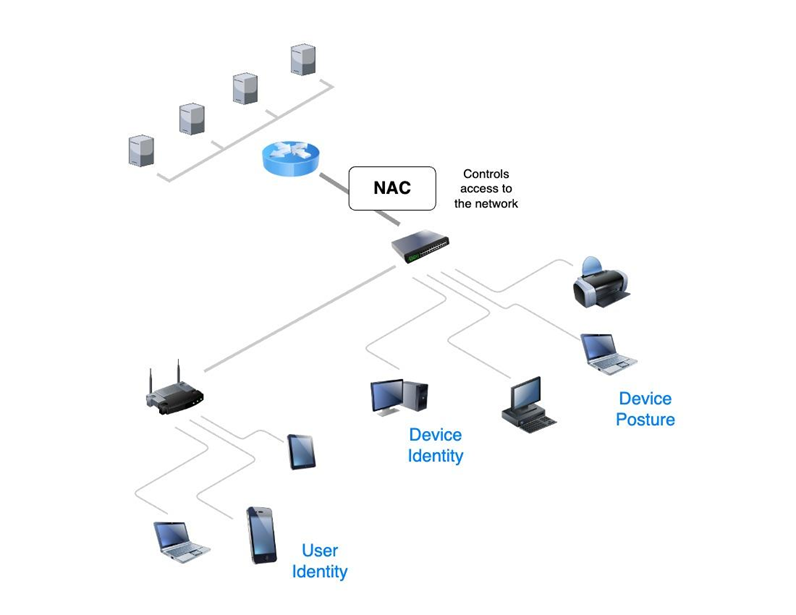
Instead of asking only, “Does this user have valid credentials?”, modern NAC asks several questions.
- Who is the user?
- What device are they using?
- Is it known and managed?
- Does it meet security requirements?
- Which systems does this person actually need?
The NAC platform uses those answers to make an access decision. A compliant employee laptop may receive normal business access. A contractor may reach only selected systems. A guest phone may receive internet access but no internal access. An unknown or infected device may be blocked or moved into quarantine.
That makes NAC in networking different from simple login control. It brings identity, device trust, network context, and security policy together when access begins.
Why Is Network Access Control Important?
The network perimeter is no longer a clear line around one office. Businesses now deal with wireless devices, BYOD, IoT systems, contractors, remote users, and shared infrastructure.
Every connection creates an important security question. Should this device be here, and what should it be allowed to access?
Without NAC, teams may know that a device joined the network but still lack useful information about its owner, health, or purpose. A vulnerable laptop or unmanaged IoT device could gain access near sensitive business systems.
A network access control system reduces this uncertainty. It improves device visibility and applies access rules based on business need and risk. Device profiling, posture assessment, restricted access, and centralized policy management are common NAC capabilities.
Want to see how Network Access Control works in real enterprise networks? Learn Cisco ISE through hands-on training.
How Network Access Control Works
Understanding how network access control works becomes easier when you follow a connection from its first request to the final access decision.
1. A User or Device Requests Network Access
The process begins when an endpoint tries to connect through Ethernet, Wi-Fi, VPN, or another supported access method.
The endpoint might be a company laptop, employee phone, printer, camera, visitor device, medical system, or industrial device.
NAC detects the connection before deciding what level of access should be available.
2. NAC Identifies the User and Device
Next step would be to identify who or what is connecting.
The identity of the user can come from login credentials, digital certificates, directory services, or single sign-on systems.
The identity of a device can come from certificates as well as network attributes, operating system information, device fingerprints and management records.
3. NAC Checks Device Security Posture
Knowing the user is not enough. A legitimate employee can still connect using an unsafe device.
Depending on company policy, NAC may check the operating system, security updates, endpoint protection, encryption, antivirus software, or device-management status.
A device that fails a required security check may receive restricted access instead of normal access. Security posture assessment is a standard capability across modern NAC platforms.
4. The Policy Engine Decides What Access Is Allowed
The policy engine compares the collected information with the organization’s access rules.
A managed finance laptop may receive access to finance systems. A personal smartphone may receive email and internet access only.
A contractor could reach one project environment. A visitor may receive internet access without reaching internal applications.
This step turns written security policies into actual network permissions.
5. The Network Enforces the Decision
The endpoint can have full access, limited access, guests access, quarantine access or even no access.
Enforcement can involve VLAN assignments as well as network segmentation, access policy, switch port controls.
Many enterprise implementations also employ technologies like IEEE 802.1X and RADIUS for the authentication process and to enforce policies.
6. NAC Can Continue Checking After Connection
Modern NAC does not need to stop working after initial authentication.
Post-admission controls can reassess access when conditions change. If a device becomes noncompliant or tries reaching a restricted network area, its permissions can be reduced or removed.
This continuous approach also makes NAC useful within broader zero trust security strategies.
Main Components of a Network Access Control System
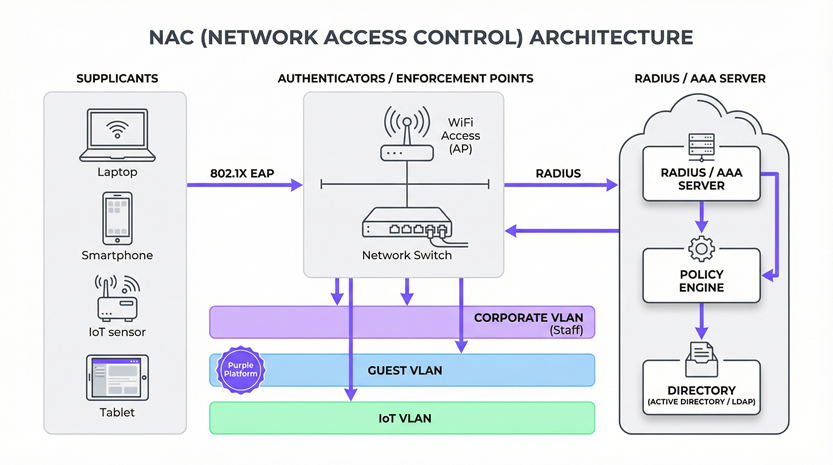
A typical network access control system involves three important functions.
The access requestor is the user or endpoint seeking network access.
The policy decision function reviews identity, device information, security posture, and company rules before deciding what should happen.
The policy enforcement point applies that decision. It may be a network switch, wireless controller, VPN gateway, or another access device.
NAC platforms can also integrate with identity directories, endpoint security products, mobile device management systems, SIEM platforms, and firewalls. These integrations provide more context for making accurate access decisions.
Types of Network Access Control
NAC is commonly divided into pre-admission and post-admission controls.
Pre-Admission NAC
Pre-admission NAC evaluates the device or user before normal network access is provided.
If the endpoint does not meet company requirements, it can be blocked, quarantined, or given limited access. This prevents clearly unauthorized or noncompliant devices from entering protected network areas.
Post-Admission NAC
Post-admission NAC applies security rules after the initial connection.
The system can reassess a device when it requests another resource, enters another network segment, or experiences a change in security status.
Using both approaches gives organizations greater control before and after network entry.
Key Benefits of Network Access Control
Better Visibility into Connected Devices
NAC helps IT teams understand what is connected, who owns it, where it connected, and what resources it can access.
This visibility becomes especially valuable when networks contain corporate devices, BYOD endpoints, guests, contractors, and IoT equipment.
Stronger Protection against Unauthorized Access
Joining the network should not automatically provide broad internal access.
NAC can block unknown endpoints, restrict risky devices, and apply different access levels according to user roles and device conditions.
Device Security Checks Before Access
A valid employee account does not guarantee that the employee’s device is secure.
NAC can include device health in the access decision. A laptop missing required security controls can receive limited access until the problem is corrected.
Safer BYOD and Guest Connectivity
Personal and guest devices cannot always be managed like company-owned equipment.
NAC allows businesses to provide useful connectivity while keeping these devices separated from sensitive systems. Guests may receive internet access, while personal employee devices receive only selected business services.
Better Network Segmentation
NAC can place users and devices into appropriate network segments based on identity, device category, business role, or security status.
This supports the principle of least privilege. Users receive the access required for their work without receiving unnecessary access to the entire network.
Faster Response to Risky Devices
A NAC platform can work with other security systems to respond when a threat appears.
For example, a device identified as compromised can be moved into quarantine automatically rather than waiting for an administrator to disconnect it manually. Automated isolation and incident response are widely supported NAC capabilities.
These automated security measures are an important part of modern enterprise network security. Build practical expertise in network security and threat response with CCNP Security training.
Common Network Access Control Use Cases
Organizations can use NAC across many different network environments.
Common examples include employee network access, BYOD programs, contractor access, guest Wi-Fi, branch offices, IoT systems, medical equipment, and industrial networks. NAC can also help isolate endpoints that become infected or fail security requirements.
NAC is particularly useful for IoT equipment because many connected devices cannot run traditional endpoint security software. The network can still identify these devices and limit where they communicate.
Frequently Asked Questions
Q1. What is network access control?
Network Access Control, or NAC is the system that controls who and what is able to connect to networks according to the type of device, identity, security status, as well as access policies.
Q2. Is NAC a firewall?
No. NAC manages access to networks to devices and users, and a firewall blocks network traffic on the basis of security guidelines. Both offer distinct levels of security.
Q3. What is ACL and types?
The Access Control List, or ACL is a list of the types of traffic that is permitted or not. Common forms include regular ACLs and extended ACLs and ACLs that are numbered ACLs as well as named ACLs.
Q4. Why is NAC required?
NAC protects against access to devices that are not authorized, and also checks the device’s security, allows BYOD control of guest connections, increases the visibility of devices, and restricts access to network resources that are sensitive.
Conclusion
Network access control gives organizations a practical way to decide who and what can enter a network, then control how far that access goes. It combines user identity, device information, security posture, and policy to make better access decisions.
A modern network access control system does more than block unknown devices. It helps identify endpoints, support BYOD, manage guest access, enforce least privilege, improve segmentation, and isolate risky devices.