
Introduction
If you work with the enterprise networks, security and access control, you must have heard of CISCO ISE many times before. Cisco ISE is used to secure access to the network, control users, provide guest access and protect the organisation from cyber attacks.
In simple terms, CISCO identity service engine (CISCO ISE) is a platform which helps organisation who connect to its network.
This matters because modern networks are no longer made up of only office desktops. Today, a business network may include:
- employee laptops
- mobile phones
- tablets
- guest devices
- VPN users
- printers
- IP phones
- cameras
- medical devices
- IoT devices
- contractor systems
What Is CISCO ISE?
A simple answer to what is CISCO ISE is this:
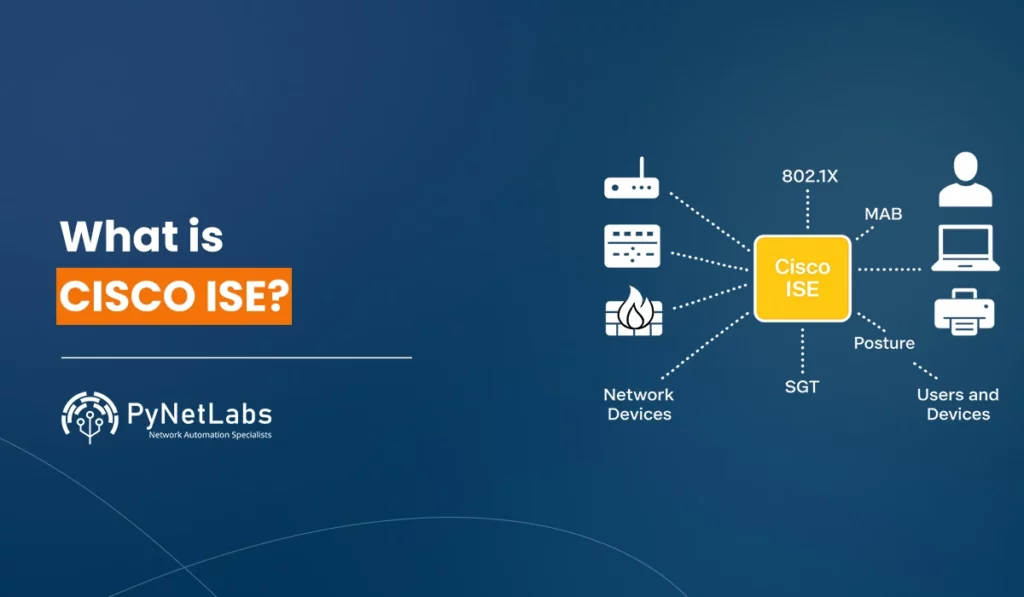
CISCO ISE is Cisco’s identity-based network access control platform.
It checks:
- who the user is
- what device they are using
- whether the device meets security rules
- where the connection is coming from
- what access should be given
Instead of treating every connection the same way, Cisco ISE helps organisations make access decisions based on identity and context.
That is why Cisco ISE is not just a login tool. It does more than verify a username and password. It also helps with:
- authentication
- authorization
- policy enforcement
- device profiling
- posture checking
- guest onboarding
- access control across wired, wireless, and VPN connections
So, when someone asks what is CISCO ISE, the best way to explain it is this: it is a platform that helps secure network access by making better decisions about users and devices.
How CISCO ISE Works?
To understand what CISCO ISE is, it helps to see how it works during a connection request.
When a user or device tries to connect, Cisco ISE looks at the request and checks different details before allowing access.
Basic working process of Cisco ISE
- A user or device tries to connect to the network.
- Cisco ISE checks identity details.
- It looks at the type of device.
- It checks whether the device meets security policy.
- It compares the request with the organisation’s rules.
- It decides what level of access should be allowed.
Based on the rule, Cisco ISE can:
- allow full access
- allow limited access
- send the user to a guest portal
- place the device in a different VLAN
- apply access control rules
- block the connection
- isolate a risky endpoint
This is what makes Cisco ISE useful in real enterprise environments. It does not only say yes or no. It gives a more controlled and flexible response.
A simple example
Let us say three different people try to connect:
- An employee with a managed office laptop
- A guest visiting the office with a personal phone
- A contractor using an unknown device
Cisco ISE does not need to treat all three in the same way.
It can:
- give the employee normal access
- send the guest to a guest internet portal
- give the contractor restricted access only to needed systems
This kind of control is one of the main reasons why organisations invest in Cisco ISE.
Key Features of CISCO ISE
Cisco ISE has many capabilities, but some features are more important than others.
1. Identity-Based Access Control
This is the core feature of CISCO ISE.
Instead of allowing access only based on where a device is connected, it uses identity and context. That means access decisions can depend on:
- user role
- device type
- location
- connection type
- policy rules
This helps organisations move away from flat access models.
2. Device Visibility and Profiling
Cisco ISE can identify and classify endpoints connected to the network. This gives security teams a clearer idea of what is actually present in the environment.
This is especially useful when the network includes:
- printers
- scanners
- IP phones
- security cameras
- IoT devices
- medical systems
Without visibility, security teams may not know what is connected. With Cisco ISE, they can make better access decisions.
3. Posture Assessment
A device may be known, but that does not always mean it is safe.
Cisco ISE can help check whether the device meets the organisation’s security requirements before granting broader access. This helps security teams avoid trusting devices that may be risky or non-compliant.
Posture checks may support decisions such as:
- full access for healthy devices
- limited access for unknown devices
- restricted access for non-compliant endpoints
4. Guest Access Management
Guest access is one of the most common business needs. Visitors often need internet access, but they should not reach internal systems.
Cisco ISE helps manage this through guest workflows and access portals. This makes it easier to offer guest connectivity without exposing the main network.
This is useful for:
- offices
- campuses
- hospitals
- schools
- event spaces
- enterprise branches
5. BYOD Onboarding
Many companies allow employees to connect personal devices. That may improve flexibility, but it also creates more risk.
Cisco ISE supports onboarding for personal devices so they can be connected in a more controlled way. Instead of allowing every personal device into the same network area, organisations can apply rules based on device type and policy.
6. Policy Enforcement
Cisco ISE does not stop at user identification. It also helps enforce the organisation’s network access rules.
This can include:
- access restrictions
- VLAN assignment
- downloadable ACLs
- redirection to portals
- segmentation-related controls
This makes Cisco ISE a practical tool, not just a reporting platform.
7. Integration With Other Security Tools
Cisco ISE can also work with wider security systems. This helps organisations share useful context such as user details, device details, or risk information.
That means Cisco ISE can become part of a broader security architecture rather than working as an isolated access product.
Main Benefits of CISCO ISE
The main value of ISE CISCO is that it brings control, visibility, and consistency to network access.
Important benefits include:
Better visibility
- Security teams can see what users and devices are connecting.
Smarter access control
- Access can be based on real conditions, not only on location.
Centralised policy management
- Rules can be created and managed in one place.
Support for zero-trust security
- Users and devices are checked before being trusted.
Better guest and BYOD handling
- Different device types can be managed more safely.
Improved segmentation support
- Users and devices can be placed into the right access zones.
More consistent security decisions
- The same policy can be applied across multiple access methods.
Support for compliance needs
- Clearer access rules and better visibility can help with reporting and audits.
For many organisations, these benefits are important because access problems often grow as the network grows. Cisco ISE helps keep that complexity under control.
Common Use Cases of CISCO ISE
Cisco ISE is useful in many real business situations.
1. Employee Network Access
Companies often use Cisco ISE to control employee access across:
- wired networks
- wireless networks
- VPN connections
This helps ensure that employees receive the right level of access based on role and device type.
2. Guest Access
Guest users need internet access, but not access to internal company systems.
Cisco ISE helps create a cleaner and safer guest experience by separating guest traffic from internal traffic.
3. BYOD Environments
When staff connect personal devices, Cisco ISE can help manage those devices with more control.
This is useful in organisations that support flexible work or mobile teams.
4. IoT-Heavy Networks
Industries with large numbers of smart devices often struggle with visibility and access control.
Cisco ISE helps identify those devices and apply different policies based on what they are and how they should behave.
5. Contractor and Third-Party Access
Contractors often need limited access to selected systems, not the full network.
Cisco ISE can support restricted access models so third-party users connect only where needed.
6. Zero-Trust Security Projects
When companies move toward zero trust, they need tools that can evaluate users and devices before granting access.
Cisco ISE fits well into that kind of security strategy.
Where CISCO ISE Fits in Enterprise Networks
Cisco ISE is designed for modern enterprise environments, not only for a single office setup.
It can be useful in:
- corporate campuses
- branch offices
- distributed enterprises
- hybrid work environments
- cloud-connected networks
- VPN-based access environments
- organisations with mixed device ownership
This flexibility is one reason why Cisco ISE remains relevant. It supports network access control across different access points and user types.
Is CISCO ISE Right for Every Organisation?
Not always.
A very small office with a simple network may not need a platform as advanced as Cisco ISE. But as the environment becomes more complex, the value becomes easier to see.
Cisco ISE is usually more useful when an organisation has:
- many users
- many device types
- guest access needs
- remote workers
- branch networks
- compliance requirements
- segmentation goals
- zero-trust plans
In these cases, managing access manually becomes harder. Cisco ISE helps bring structure and policy to that process.
Things to Consider Before Deployment
Cisco ISE is powerful, but it also needs planning.
Before deployment, organisations should think about:
- user groups
- device categories
- authentication sources
- access rules
- guest workflows
- posture requirements
- enforcement actions
- segmentation goals
If these areas are planned properly, Cisco ISE can deliver strong results. If not, the setup may become harder than expected.
So, while Cisco ISE offers many benefits, it works best when it is treated as a strategic security platform, not just another network tool.
Frequently Asked Questions
Q1. What is CISCO ISE used for?
Ans. Cisco ISE is used to control the access of network by checking the users identity, type of device, security status and by applying policy rules before granting any access to user.
Q2. Is Cisco ISE only for large enterprises?
Ans. It is the most useful for the medium and the large organisation, but any business with complex network access, guest users can take benefit from using CISCO ISE.
Q3. Does Cisco ISE support guest and BYOD access?
Ans. Yes, CISCO ISE supports the guest portal and BYOD onboarding. Which help organisations to give controlled access to its visitors and personal devices without the any risk of internal system.
Q4. Why is Cisco ISE important for zero trust?
Ans. Cisco ISE support zero trust by verifying users and devices prior to providing access and enforcing context based policies and avoiding automatic trust.
Conclusion
Cisco ISE is a platform for the identity based access to network and control it. It helps organisations check the users and devices on their network by applying security polices and rules. Its real value comes from managing the network in controlled manner where user have limited access without the risk of any internal security leak. Which protect companies from being targeted by hackers and various cyber attacks.