
What if one security strategy could not protect every network from every threat? That is where Network Security Models come into play, providing structured approaches to control access, protect data, and reduce security risks. From traditional perimeter-based security to modern Zero Trust frameworks, these models help organisations build stronger and more resilient networks.
As cyber threats continue to evolve, understanding how different Network Security Models work has become essential for network and security professionals. For aspiring Network Security Engineers, learning these models is equally important, as they provide the foundation for designing, securing, and managing modern network environments. In this blog, we will explore the major security models, their key principles, how they work, and where they fit into modern network security strategies.
Let us begin by first understanding what exactly a model for network security is.
What Is a Network Security Model?
A Network Security Model is a framework that defines how different security measures work together to protect a network, its devices, applications, and data. It provides a structured approach to managing authentication, access control, encryption, threat detection, traffic filtering, and security monitoring.
A network security model also establishes how trust and security controls are organised across users, endpoints, network segments, cloud environments, and data centres. Its primary goal is to protect the confidentiality, integrity, and availability of network resources while preventing unauthorised access and reducing security risks.
Core Components of the Network Security Model
The Network Security Model combines several components. These are:
| Component | Role in the Network Security Model |
| Sender/User | Starts communication or requests access |
| Authentication | Verifies the identity of users, devices, or services |
| Authorisation | Determines what an authenticated entity can access |
| Security Transformation | Uses encryption, signatures, hashing, or other mechanisms |
| Secret Information (Keys/Credentials) | Provide information needed by security mechanisms |
| Network Channel | Carries information between systems |
| Security Controls | Firewalls, ACLs, IDS/IPS, gateways, and segmentation enforce policy |
| Monitoring | Records and analyses network activity |
| Recipient/Resource | Receives the message or requested connection |
| Trusted Third Party (TTP) | May support certificates, identity verification, or key distribution |
The architecture should support specific security services rather than simply adding more tools.
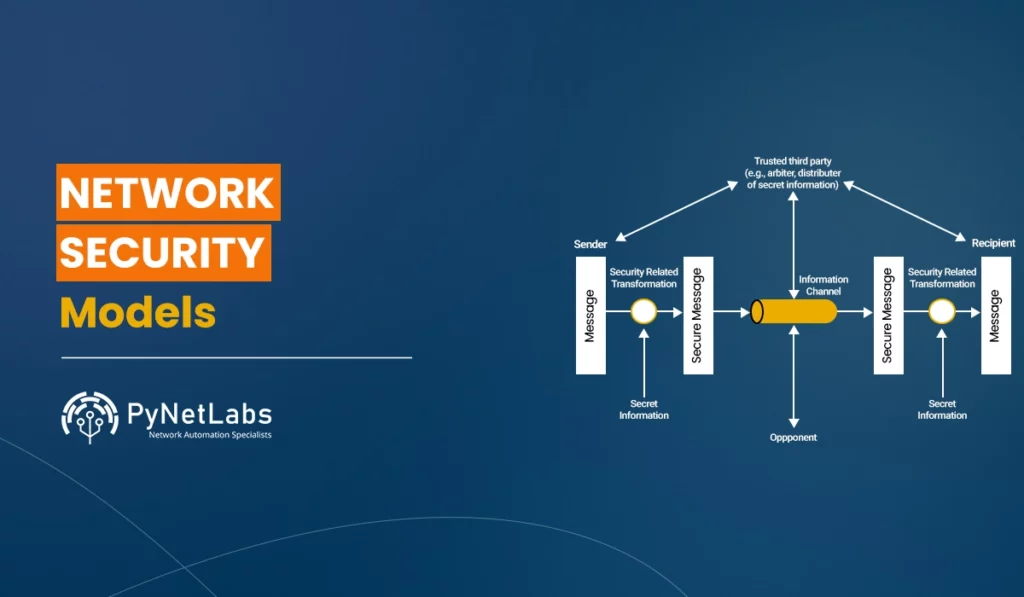
Network Security Model Diagram
The diagram illustrates the cryptographic network security model, showing how a message is protected while travelling through an untrusted communication channel.
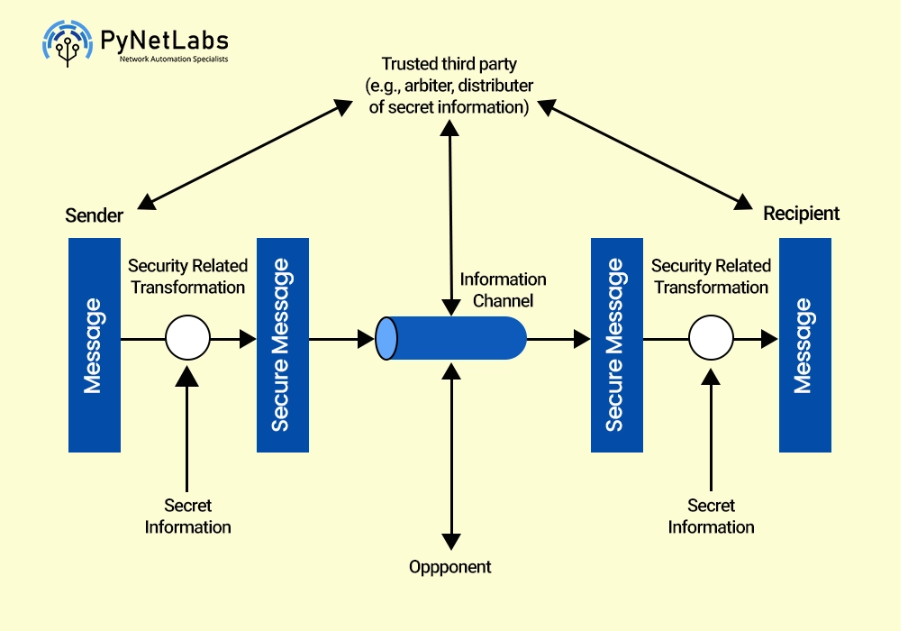
- Sender: Creates and sends the original message.
- Security-related Transformation: The sender applies a security process such as encryption using secret information (a key).
- Information Channel: The protected message travels through the communication channel.
- Opponent: Represents an attacker who may attempt to intercept or compromise the communication.
- Recipient: Receives the secure message and applies the corresponding security transformation, such as decryption, using the required secret information.
- Trusted Third Party: Helps establish trust between the sender and recipient, such as by distributing or managing secret information.
How Does a Network Security Model Work?
A Network Security Model usually works through a series of interconnected stages:
- Identify the Parties: The network determines which device, user or application is requesting communication.
- Authenticate: Credentials, certificates, MFA, tokens or device identity can be verified.
- Apply access policy: The system decides whether a person who is requesting the resource can connect to the resource.
- Protect the Information: Hashing, encryption, authentication of messages or digital signatures could be used.
- Transmit the Data: The information that is protected is transmitted through an internal network, Internet, wireless network or even the cloud.
- Enforce Security Controls: Firewalls, IDS/IPS, gateways, ACLs, and segmentation rules are used to monitor or block the traffic.
- Verify the Communication: The destination decrypts or validates the information received.
- Monitor Activity: Monitoring tools and networks logs assist in identifying abnormal behaviour.
Note: The way these stages are implemented is dependent on the architecture chosen.
In enterprise networks, platforms such as Cisco ISE can help enforce these access decisions by authenticating users and devices and applying identity-based policies. For professionals looking to build these practical skills, Cisco ISE Training provides hands-on experience with network access control.
What is Network Security Architecture and how is it Structured?
The network security architecture is the structure of trust, zones, controls and data policy that connect software rules with physical hardware to control the flow of traffic. Important structural elements include:
- Logical Access Controls: Models such as Bell-Lapadula ensure confidentiality, and Biba assures security.
- Business Transaction Logic: Clark-Wilson enforces separation of duties and Brewer-Nash builds the dynamic Chinese Walls to prevent conflicts of interest.
- Infrastructure Layouts: The DMZs offer buffer zones and ACLs control network traffic.
This approach secures data boundaries and separates the private and public network segments.
What is Network Security Model in Cryptography?
A Network Security Model in cryptography explains how cryptographic techniques can be used to protect communication between a recipient and sender via a non-secure network.
Cryptography supports the model through mechanisms such as:
- Encryption protects message confidentiality.
- Hashing helps detect changes in data.
- Digital Signatures help verify the message’s authenticity and source.
- Cryptographic keys control encryption, decryption, signing, and verification.
- Key distribution makes sure that the keys needed get to the right people safely.
- Trusted third parties as certificate authorities or key distribution services can help build trust.
Example: HTTPS follows the same basic idea. The cryptographic protocols, certificates, algorithms, and keys are all used to secure communication between browsers and a web server.
What are the Different Types of Network Security Models?
Different environments have their own ways to manage security in networks. Below, we have discussed the most important types of Network Security Models.
1. Perimeter Security Model
A perimeter security model is designed to provide security around the boundaries of an organisation’s network.
It is also known by the name castle-and-moat model. Security firewalls, VPNs, proxy servers and intrusion prevention systems establish a security boundary between internal security systems that are trusted and external networks that are not trusted.
Weakness: When a person or a threat is detected within the perimeter the structure may allow the attacker more access than is necessary.
Example: Employees connect to the network of the company via VPN, and gain access to various internal applications.
2. Defence-in-Depth Model
Defence-in-depth offers multiple layers of protection across the entire environment.
For example, an organisation might use:
- A firewall at the Internet edge
- MFA for user accounts
- Endpoint protection on laptops
- Network segmentation between departments
- Encryption for sensitive information
- IDS/IPS for detecting suspicious traffic
- SIEM monitoring for centralized visibility
In the event that one layer fails, another layer is still able to prevent the attack, identify it, or even limit the threat.
Example: Malware bypasses an email filter, but it is blocked with endpoint protection. If an endpoint has been damaged, the network segmentation may be able to block it from reaching critical servers.
3. Zero Trust Security Model
Zero Trust changes the basic trust assumption.
A device or user is not considered reliable simply because it’s connected to a corporate network. Access is determined by the identity of the user, the condition of the device, permissions, context and various security signals.
Example: Remote employees request access to an HR app. The system validates the identity of the employee, their MFA, device health and authorises access only to that particular application.
Learning how these capabilities are configured on next-generation firewalls is an important step for professionals looking to build practical network security skills, making Palo Alto Firewall Training a relevant path for gaining hands-on experience.
4. Network Segmentation and Micro Segmentation
Network segmentation breaks up a huge system into smaller zones of security.
For instance, guest Wi-Fi, devices for employees, financial systems, development servers, and production databases are placed into separate sections. The policies then determine which segments can be allowed to communicate.
Micro Segmentation is a variant of the same idea on a much more detailed level. Every single application, task, or devices could be governed by their own access policies.
This makes lateral movement more difficult if one of the endpoints is compromised. Segmentation is often utilised as a part of Zero Trust and defence-in-depth architectures.
How to Choose the Right Model for Network Security?
There is no single Network Security Model architecture that is appropriate for every business. Take into consideration the following aspects in deciding on the appropriate strategy:
- Determine the Environment you are in: Determine where users, devices, applications, sensitive information, as well as workstations are.
- Examine Communication Paths: Identify which systems and users really require interaction with one the other.
- Consider Your Network Setup: An organisation that is primarily based out of only one physical location may keep using robust perimeter controls. But it must be able to limit internal trust and separate sensitive resources.
- Consider Cloud and Remote Access: Organisations using cloud platforms, SaaS applications, and remote workers and have multiple locations typically require access controls based on their identity.
- Use the Appropriate Security Controls: Zero Trust principles such as segmentation, least privilege, encryption and continuous monitoring are more crucial in distributed environments.
- Utilise a Multi-layered Approach: In practice, the combination of multiple security strategies is more often effective. Zero Trust can be used to control access decisions, segmentation may limit lateral movement, cryptography can secure communications, and defense-in-depth can offer additional security when one security measure is not working.
Conclusion
A Network Security Model provides a structured way to protect data, communication, users, devices, and network resources from different types of threats. Depending on the environment, organisations may use perimeter security, defence-in-depth, Zero Trust, segmentation, or cryptographic mechanisms to reduce risk. The right approach depends on network design, access requirements, data sensitivity, and business needs. In practice, combining multiple security controls and models provides stronger protection than relying on a single method.
Frequently Asked Questions
Q1 What are Network Security Models?
A Network Security Model can be defined as a framework that explains how you can achieve a data transmission as well as data communication over an insecure channel.
Q2 What are the 7 Types of Networks?
Seven types of networks are LAN, MAN, PAN, WLAN, CAN, SAN, and WAN.
Q3 What are the 7 Types of Security?
The seven types of security are network security, physical security, endpoint security, cloud security, data security, application security, and human layer security.
Q4 What is the CIA Triad Model of Network Security?
CIA triad model of network security focuses on three crucial aspects including confidentiality, Integrity, and authenticity.