Network security architecture is the structured design used to safeguard the network, its users, apps, devices, and data from unauthorised access as well as cyberattacks. It determines where security control points are located, the way traffic is moved, who is able to connect and how suspicious activity can be identified.
A well-designed architecture extends beyond placing a firewall on the internet edge. It integrates access control and segmentation, as well as threat detection and encryption, endpoint security, monitoring, and recovery to form a single connected system. This is particularly important for organizations that use cloud-based services, mobile devices, remote access as well as multiple locations.
In this blog, we will discuss what network security architecture is, its components, diagram, and best practices you can use in order to design a secure network.
What is Network Security Architecture?
Network security architecture is a blueprint for securing communication between users, devices, applications, servers, cloud resources, and external networks.
It covers both network layout and the security rules applied to it. In practical terms, it answers questions such as:
- Who and what can connect to the network?
- Which systems can they access?
- Which areas should remain separated?
- Where should traffic be inspected?
- How will suspicious behavior be detected?
- How will data be protected in transit?
- What happens if one account or device is compromised?
The aim is not to depend on one security product. Several controls work together so that if one fails, another can block, detect, or contain an attack. This is the basic idea behind defense in depth.
Modern architecture also avoids assuming that anything inside the company network is automatically safe. NIST’s Zero Trust guidance says trust should not be granted simply because a user or device is on an internal network. Access should be verified before a resource is reached.
Why Network Security Architecture Matters Now
Attacks are cheaper to launch than ever, and networks are harder to defend. Staff work from home, applications run in several clouds, and personal devices connect daily. A planned architecture gives you three advantages:
Consistent protection: Every zone follows the same rules, so nothing depends on one admin’s memory.
Faster response: When something goes wrong, you know where the controls are and what they saw.
Easier audits and growth: Compliance checks and new rollouts go smoothly when the design is documented.
Without architecture, each new tool adds complexity instead of safety.
Core Components of Network Security Architecture
The products organizations use can vary however the functions remain the identical.
1. Firewalls
Firewalls filter the flow of traffic between zones according to guidelines you specify. The next-generation firewalls (NGFWs) take it a step further by looking at traffic at application layer and preventing attacks. Install them on the network edge and in between the internal zones.
2. Intrusion Detection and Prevention Systems (IDS/IPS)
An IDS monitors the traffic of a system and warns you if it notices anything that is suspicious. An IPS can go further, blocking the flow of traffic on a real-time basis by identifying what your firewall allows to pass.
3. Network Segmentation
Segmentation is the process of dividing a large network into smaller segments by using VLANs, Subnets, or micro-segmentation. If a hacker compromises the one segment, they are unable to move around the other segment. This reduces the impact from almost every attack.
4. Identity and Access Management (IAM)
IAM determines who is allowed to get inside and what series of activities they can do. The most important components are multi-factor authentication (MFA) as well as Role-based access control (RBAC), and least-privilege permissions. All these components ensure devices and users are granted access only that is required for their work.
5. Secure Remote Access
Remote users are connected via VPNs or, in more modern design, Zero Trust Network Access (ZTNA). ZTNA checks identity and device performance for each request instead of relying on anyone who has a VPN password.
6. Encryption
Encryption protects data while it is in transit (TLS, IPsec) and in the rest (disk and database encryption). The traffic that is intercepted or stolen is not readable.
7. Endpoint Security
Each laptop, smartphone, or server serves as the entry point. Endpoint detection and Response (EDR) as well as anti-malware and device management help keep devices free of malware before they even touch the network.
8. Monitoring and SIEM
Security Information and Event Management (SIEM) platforms gather and combine logs from each component. This is the way to identify the attack which spans 5 systems and looks harmless in all of them.
9. Data Loss Prevention (DLP)
DLP tools track the movement of sensitive data and stop attempts to transmit data outside of channels that are approved.
Understanding the Network Security Architecture Diagram
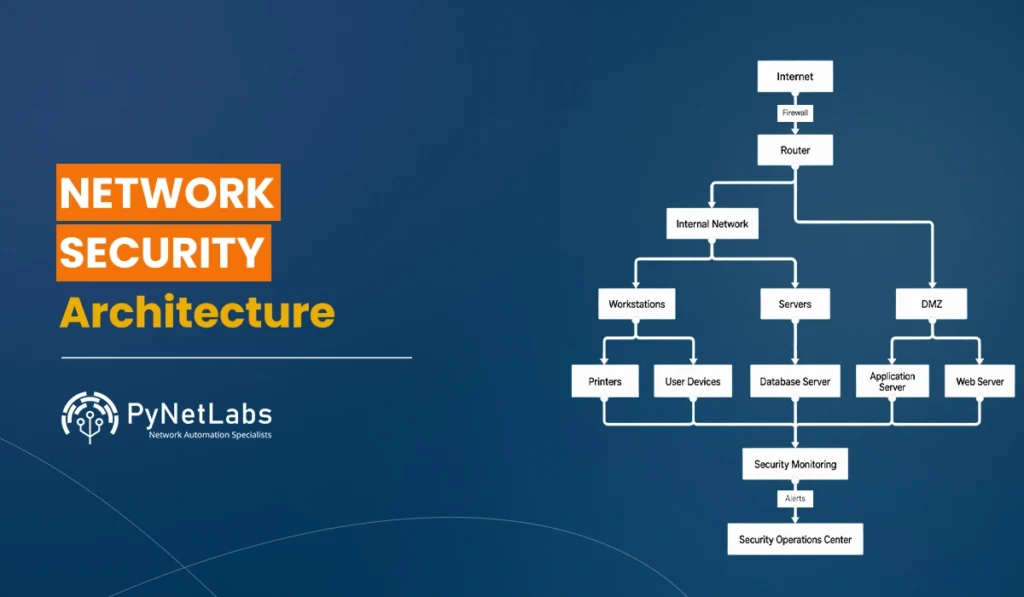
The network security architecture diagram is visual representation of the components involved and how they are connected. The diagram helps teams identify the flow of traffic, trust boundaries, network zones, as well as possible attack paths. You cannot defend when you cannot see it and this is the main reason why this map is an essential document for security professionals.
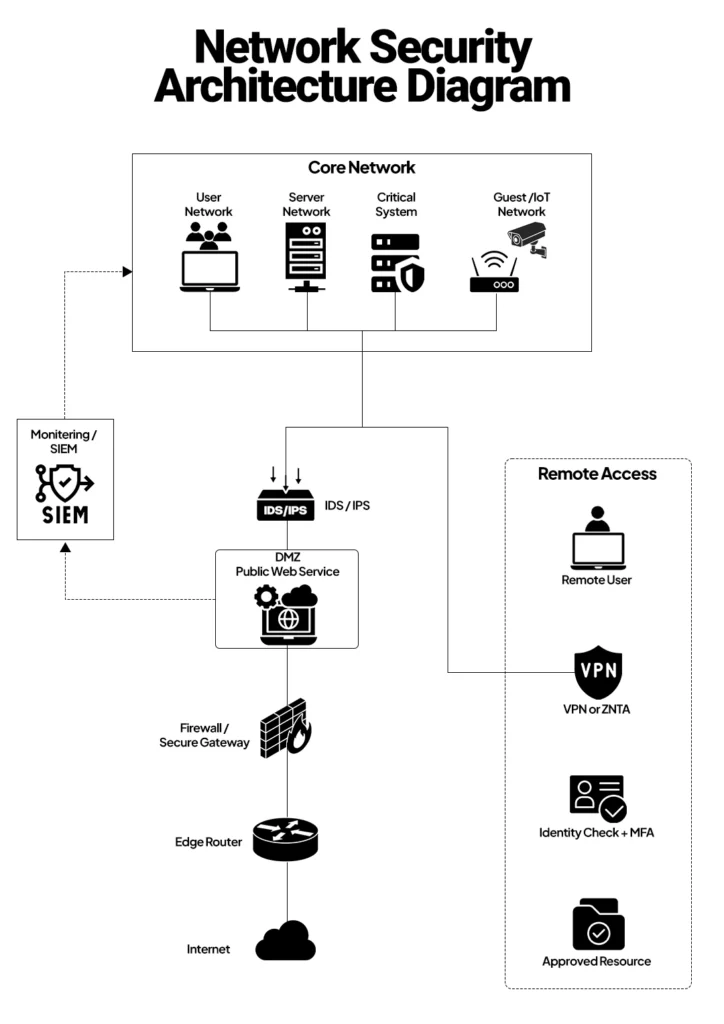
When you read the diagram, you should follow the flow of the traffic. Find out where the flow enters, which controls are examining the flow, and what zones it crosses. The trust boundaries, where traffic passes between zones, are where your enforcement points belong. A path with no control on it is a gap.
Common Network Security Architecture Models
A majority of businesses choose one model or mix them together.
Perimeter-based model: It follows the traditional approach. It combines robust security at the edges and a reliable or trusted network within. It has a difficult time with cloud and remote work, as “inside” barely exists anymore.
Defense in depth: Overlapping layers of controls so that the failure of one control will be spotted by the next. It is the foundation of nearly every solid design.
Zero Trust: It is the current standard and it assumes breaches and removes all implicit trust. Every user, device and request is verified every moment, with the use of least-privilege access and continuous validation.
SASE (Secure Access Service Edge): Security and networking combined into a cloud-based service that is suited for distributed teams and heavy use of cloud.
In the majority of teams, the most practical option is defense in depth, with a phased move toward Zero Trust.
How to Design Network Security Architecture
Good design follows a process. The lack of attention to details is the reason gaps appear.
Step 1: Inventory Your Assets and Data Flows
Make a list of every device, application as well as data storage facility and track how data flows across them. You can expect to discover forgotten systems and unexpected connections.
Step 2: Define Zones and Trust Levels
Group assets according to their functions and sensitivity, then determine which zones can be able to communicate with one another. Critical databases and public servers must not share one zone.
Step 3: Place Controls at the Boundaries
Set up firewalls, IPS and access control where zones commonly meet. Each trust boundary requires enforcement and surveillance.
Step 4: Enforce Strong Identity Rules
The rollout of MFA should be applied everywhere not only for administrators. Utilize the least privilege through RBAC as well as examine access rights according on a schedule.
Step 5: Plan for Detection and Response
Consider that certain attacks are likely to get through. Consolidate logs into an SIEM, create alert rules, and write the response plan in advance of when you’re required to use it.
Step 6: Document Everything
Produce the network security architecture diagram and the logic for the diagram. Documentation transforms tribal knowledge into an asset for the team.
Step 7: Test and Review Regularly
Conduct penetration and vulnerability tests. Re-evaluate the structure after significant modifications like cloud migration.
Network Security Architecture Best Practices You Should Know
These practices apply to almost every environment:
1. Layer your defenses: It is crucial for every network professional while designing network architecture is to never ever rely on a single control. Always combine perimeter, internal, endpoint, and application security.
2. Segment aggressively: The flatter the network, the faster an attacker moves. So, always segment your big network into smaller networks to stop the attack to only one segment.
3. Patch on a schedule: You should update your systems on a regular basis as unpatched systems remain a top breach cause in modern security.
4. Require MFA for everyone: Stolen passwords stop mattering when a second factor stands in the way.
5. Encrypt by default: Always protect data that is in transit or at rest, and side-by-side it is highly recommended to manage keys with care.
6. Watch the logs daily: A SIEM that nobody reads is shelfware.
7. Remove old rules and accounts: Firewall rule sets and user directories grow as network size increases. So, always try updating them regularly and side-by-side remove the old ones.
8. Back up and test recovery: Ransomware makes backups your last line of defense. Test restores, not just backups.
9. Train your people: Phishing still beats most technical controls.
10. Keep the diagram current: Always update the network security architecture diagram after every infrastructure change. It should be updated as new attacks always try to penetrate the system.
Frequently Asked Questions
Q1. What are the three types of network architecture?
Ans – The three types of network architecture are Peer-to-Peer, Client-Server, and Hybrid model.
Q2. What are the 7 layers of network security?
Ans – The 7 layers of network security are physical, perimeter, network, endpoint, application, data, and human & Identity.
Q3. What are types of security architectures?
Ans – Different types of security architecture are network security architecture, cloud security architecture, application security architecture, endpoint security architecture, enterprise information security architecture, and wireless security architecture.
Q4. What are the 7 types of security?
Ans – The 7 types of security are physical security, network security, application security, information security, operational security, cloud security, and endpoint security.
Conclusion
Network security architecture describes how an organisation protects its network as a whole rather than the collection of a set of different devices. The best design shows the devices, users, applications and data reside in relation to each other, the way they connect with each other, and the controls that safeguard each one of them.
Network security architecture diagram should not remain static. Threats, networks, and access needs are constantly changing so does the design.