
Preparing for MPLS interview questions in 2026 requires more than learning the basic definitions. Interviewers may start asking about labels, LDP, LSPs, and router roles. However, more experienced candidates are frequently given network scenarios that involve missing routes, broken LDP sessions, VRF issues, and MPLS VPN connectivity. The best way to prepare is to understand what happens to a packet from the moment it enters an MPLS network until it leaves.
In this blog, we will discuss the most asked MPLS interview questions and answers that covers MPLS VPNs, label forwarding, troubleshooting and practical scenarios that you might encounter during the interview.
MPLS Interview Questions and Answers: Beginner- Level
Q1. What do you understand about MPLS?
MPLS full form is Multiprotocol Label Switching. MPLS is forwarding technology that assigns packet labels when they enter an MPLS network.
Routers in the MPLS domain are able to use these labels in making forwarding decisions.
MPLS is associated with service provider networks. The reason behind this is it assists providers in building scalable VPN services that separate customer traffic, support traffic engineering and manage the way traffic flows through their backbone.
Q2. Why is MPLS called a Layer 2.5 technology?
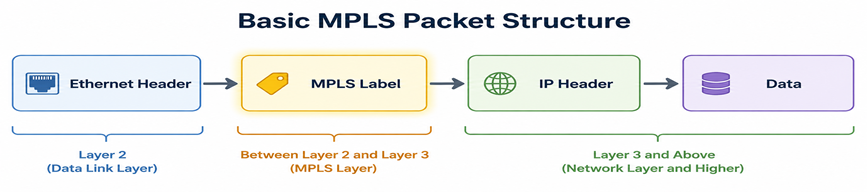
MPLS is commonly described as a Layer 2.5 technology because the MPLS label sits between the Layer 2 header and the Layer 3 packet.
It does not actually create a new OSI layer. “Layer 2.5” is simply an easy way to describe its position.
Q3. What is an MPLS label?
An MPLS label is a 32-bit or 4-byte label stack entry inserted into a packet.
It contains:
- 20-bit Label Value
- 3-bit Traffic Class field
- 1-bit Bottom of Stack field
- 8-bit TTL field
The Traffic Class field was earlier known as the EXP field. It was officially changed by RFC 5462 to the Traffic Class field.
The value of the label is what MPLS routers use for making decisions about which way to send the data.
Q4. Does an MPLS packet have a fixed size?
No. There’s no set MPLS packet size.
It is an effective trick as candidates often mistake the MPLS label size with the size of the whole packet. Every MPLS label stack entry adds four bytes to the entire packet. When two labels are utilized, MPLS adds 8 bytes. When there are three labels and it is used, MPLS will add 12 bytes.
Q5. What are the main router types in an MPLS network?
It is common to hear three terms used in routers:
- CE (Customer Edge): It is located on the client side and is connected with the provider.
- PE (provider edge): Connects the customer’s networks with the service provider’s MPLS network.
- P (Provider Router): Functions within the provider core.
A router that is a P doesn’t require the customer’s VPN routing data. It mostly forwards traffic over the provider network through MPLS labels.
This separation is one of the reasons MPLS VPN architectures can scale very well.
Q6. What are LER and LSR in MPLS?
An LSR (also known as Label Switching) Router is a router that forwards packets with labels within MPLS networks.
A LER, also known as Label Edge Router works at the MPLS boundary.
An Ingress LER may add labels when the packet enters within the MPLS domain. An egress LER eliminates any remaining MPLS information prior forwarding the packet outside the MPLS domain.
Q7. What are push, swap, and pop operations in MPLS?
These are the three basic MPLS label operations.
- Push: A label is added to the packet.
- Swap: The incoming label is replaced with another label.
- Pop: A label is removed.
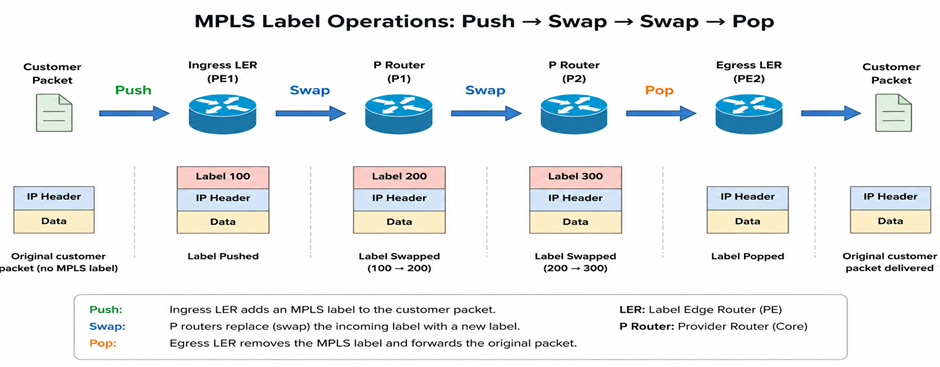
Do not only memorize these terms. Interviewers may ask you which device performs each action during an actual packet journey.
Q8. What is FEC in MPLS?
FEC means Forwarding Equivalent Class. It represents the packets that should receive the same forwarding treatment. Instead of interpreting every packet as a separate entity, MPLS can map packets that belong to a specific FEC to an LSP.
For example, several packets heading to the same destination with the same prefix may belong to the same FEC thus using the same route to forward.
LDP associates labels with FECs while building label-switched forwarding.
Q9. What is an LSP?
LSP is a short form for “Label Switched Path“. It’s the route that a labeled packet follows within the MPLS network, from ingress toward egress.
An important detail for your interview is to remember that you shouldn’t ever define the LSP as a manually “predefined path.”
When using normal LDP-based MPLS, the forwarding paths generally follow the one chosen by the underlying IGP. Other MPLS technologies can provide more explicit path control.
Q10. What is LDP?
LDP refers to “Label Distribution Protocol”. MPLS routers require a method to inform neighboring routers that labels are associated with particular FECs. LDP is a standard method to exchange these label bindings.
LDP thus works in conjunction with the routing protocol instead of replacing it.
The IGP decides on reachability as well as the next hops. LDP distributes labels that can be utilized along these normally routed paths.
MPLS Interview Questions and Answers: Advanced-Level
Q11. What is the difference between IP forwarding and MPLS forwarding?
The basic difference between the two, i.e., IP and forwarding and MPLS forwarding is:
| Factor | IP Forwarding | MPLS Forwarding |
| Forwarding basis | Destination IP address | Top MPLS label |
| Lookup | IP forwarding table | Label forwarding table |
| Packet action | Forwards to next hop | Push, swap, or pop label |
| Path decision | Based on IP routing | Based on label-switched path |
| Core visibility | May require destination route knowledge | Core can forward without customer VPN routes |
| Traffic engineering | Limited in standard IP routing | Supports traffic engineering |
| VPN support | Needs additional mechanisms | Commonly used for MPLS VPNs |
| Scalability | Suitable for normal IP networks | Well suited for large provider networks |
| Common use | Enterprise and internet routing | Service provider backbones and VPNs |
Q12. What are LIB and LFIB?
These terms often appear in technical interviews.
LIB full form is Label Information Base
It contains label bindings learned or generated by the MPLS control plane.
LFIB full form is Label Forwarding Information Base
It contains the information actually used to forward labeled packets.
Think of LIB as the available label knowledge and LFIB as the forwarding instructions derived from that information.
Note: When troubleshooting, seeing labels in the control plane does not automatically prove that forwarding is working correctly.
Q13. What is Penultimate Hop Popping?
Penultimate Hop Popping, or PHP, means the second-last MPLS router removes the transport label before sending the packet to the egress router.
Suppose the path is:
PE1 → P1 → P2 → PE2
P2 is the penultimate router.
Instead of sending PE2 a packet carrying a label that PE2 would immediately remove, P2 can remove that label first. PHP can be defined as a way for the router before the egress LSR to remove the label.
Q14. What is an implicit-null label?
The implicit-null label has reserved label value 3.
It effectively tells the upstream router: Remove this label before sending the packet to me.
This is how normal PHP behavior is signalled.
The important interview point is that label 3 is generally advertised but is not carried on the wire as a normal top label for forwarding toward that destination.
Q15. What is an explicit-null label?
An explicit-null label allows the packet to remain labeled until it reaches the egress router instead of using normal PHP.
For IPv4, label 0 is the IPv4 Explicit NULL label.
One reason an operator may use explicit null is to preserve MPLS Traffic Class information through to the egress device for QoS handling.
Q16. What is label stacking in MPLS?
MPLS can carry more than one label. The labels form a label stack. This is particularly useful when one label is needed to transport the packet across the provider network while another identifies a service or VPN.
The Bottom of Stack bit identifies the final MPLS label in that stack. Label stacking is therefore not simply “adding extra labels.” Each label can have a separate forwarding or service purpose.
Q17. Does MPLS replace OSPF or IS-IS?
No. MPLS is dependent on an underlying network that is already aware of how to reach destinations.
Protocols like OSPF and IS-IS are often used as the IGP within a provider network. They offer IP reachability across routers. MPLS then creates label forwarding on top of this reachability.
A simple way to understand it is:
IGP discovers the right path. MPLS labels assist in forwarding traffic over that path.
Q18. What is an MPLS Layer 3 VPN?
A MPLS Layer 3 VPN enables a service provider to link customer sites using their shared network of MPLS backbone, while keeping separate routing details for various customers.
PE routers manage the customer-specific routing contexts as well as Exchange VPN routing paths via MP-BGP. One of the advantages is the fact that P routers that are part of the provider’s core don’t require VPN route for every customer.
The provider core generally requires sufficient information in order to deliver the labeled pack to the correct PE.
Q19. What is a VRF?
VRF full form is Virtual Routing and Forwarding. A VRF gives a router a separate routing and forwarding table.
For example, a PE router might contain:
Customer-A VRF
10.1.0.0/16
Customer-B VRF
10.1.0.0/16
Both customers can use the same address range because their routing information is stored separately. This ability to isolate routing tables is fundamental to MPLS Layer 3 VPN services.
Q20. What is a Route Distinguisher?
A Route Distinguisher or RD makes customer prefixes unique when they are carried through MP-BGP.
Suppose two customers both advertise:
10.1.1.0/24
Their IPv4 prefixes overlap.
Adding different RDs turns them into unique VPN routes so BGP can distinguish between them.
The key interview point is this:
RD provides uniqueness. It does not decide which VRF should receive the route.
Q21. What is a Route Target?
A Route Target or RT is used to control VPN route import and export policies.
When a PE exports a VPN route, an RT can be attached to it. Another VRF imports that route when its import policy matches the appropriate Route Target. That gives the provider control over which VPN sites can exchange routing information.
Q22. What is the difference between RD and RT?
This is one of the most important MPLS interview questions.
Remember it this way:
RD = Uniqueness
RT = Routing Policy
The RD prevents identical customer prefixes from becoming identical VPN routes. The RT determines who imports or exports those VPN routes.
Do not answer that both are simply used to separate customers. That misses their different jobs. A network can even use the same-looking numeric format for RD and RT, but their purposes remain different.
Q23. What is the role of MP-BGP in MPLS Layer 3 VPN?
MP-BGP transmits VPN routing information between PE routers. It carries information like VPN prefixes as well as Route Distinguishers, Route Targets and associated service labels.
PE routers thus can learn VPN routes of remote customers and do not require P routers to be able to carry these customers’ routes. As per the RFC 4364 model, customer routes reach PE routers whereas BGP can be used in the provider network to share VPN routing information among PEs.
Q24. Why are two MPLS labels commonly seen in an L3VPN packet?
A typical MPLS Layer 3 VPN packet may contain:
Outer Label = Transport Label
Inner Label = VPN or Service Label
The outer label helps move the packet across the provider core toward the correct egress PE. The inner label helps the egress PE determine how the VPN traffic should be handled.
MPLS Interview Questions and Answers: Scenario-Based
Q25. The IGP is working, but the LDP neighbor is down. What would you check?
First confirm basic IP connectivity between the MPLS routers. Then check:
- Is MPLS/LDP enabled on the correct interfaces?
- Are LDP router IDs reachable?
- Is the LDP discovery process working?
- Is TCP connectivity required for establishing the LDP session available?
- Are ACLs or security policies blocking LDP?
- Is there an interface or configuration mismatch?
The important approach is to separate the problem into IP reachability, LDP discovery, session establishment, and label exchange rather than randomly changing MPLS configuration.
Q26. The VPN route exists on one PE but not on the remote PE. How would you troubleshoot it?
Follow the route through the control plane. Check whether:
- The CE route entered the correct VRF.
- The PE exported it into MP-BGP.
- The VPN route has the expected RD and RT.
- The MP-BGP session is established.
- The remote PE received the VPN route.
- The remote VRF has the correct import RT.
This method tells the interviewer you can trace where a route disappeared instead of simply saying, “Check BGP.”
Q27. The remote PE receives the VPN route, but it is not appearing in the customer’s VRF. What is a likely cause?
A Route Target mismatch is one of the first things to check. The remote PE may successfully receive the VPN route through MP-BGP, but the destination VRF will not automatically import every VPN route. Its import policy must match the relevant RT.
Also check route validity, next-hop reachability, routing policy, and any platform-specific restrictions. The important clue is that MP-BGP receiving the route and the VRF importing the route are separate stages.
Q28. Routes and labels look correct, but customer traffic is still failing. What would you check next?
Do not stop troubleshooting simply because the routing tables look correct. Check the data plane:
- MPLS forwarding entries
- Interface status
- Next-hop resolution
- Label operations
- MTU
- Packet drops
- ACLs
- QoS policies
- Return path
- CE routing
An MTU problem is especially worth checking because every MPLS label adds four bytes.
A good network engineer proves both control-plane health and data-plane forwarding before declaring the MPLS network healthy.
Q29. Is MPLS encrypted?
No. MPLS can provide traffic separation, but traffic separation is not the same as encryption.
An MPLS VPN can keep one customer’s routing data separate from another customer’s routing data. However, the MPLS label does not encrypt the packet payload itself.
If a company requires privacy to protect against interception of packets, encryption technology like IPsec might be necessary depending on design and security needs.
Q30. What is SR-MPLS, and why should an MPLS engineer know it in 2026?
SR-MPLS means Segment Routing over the MPLS data plane.
Instead of relying only on traditional MPLS signalling methods for building paths, Segment Routing can encode instructions as a sequence of MPLS labels called segments or Segment IDs.
It reduces some of the signalling state traditionally required in MPLS traffic-engineering designs and gives operators powerful path-control options.
Conclusion
The best way to prepare yourself for MPLS interview questions is to be aware of the entire path of the packet rather than attempting to remember a dozen questions. Start with the labels, FECs, LSPs, LDP as well as router roles. After that, move onto VRFs as well as MP-BGP, RDs, RTs, and MPLS VPN forwarding. Then, practice troubleshooting scenarios where routing, labels or customer connectivity fails.