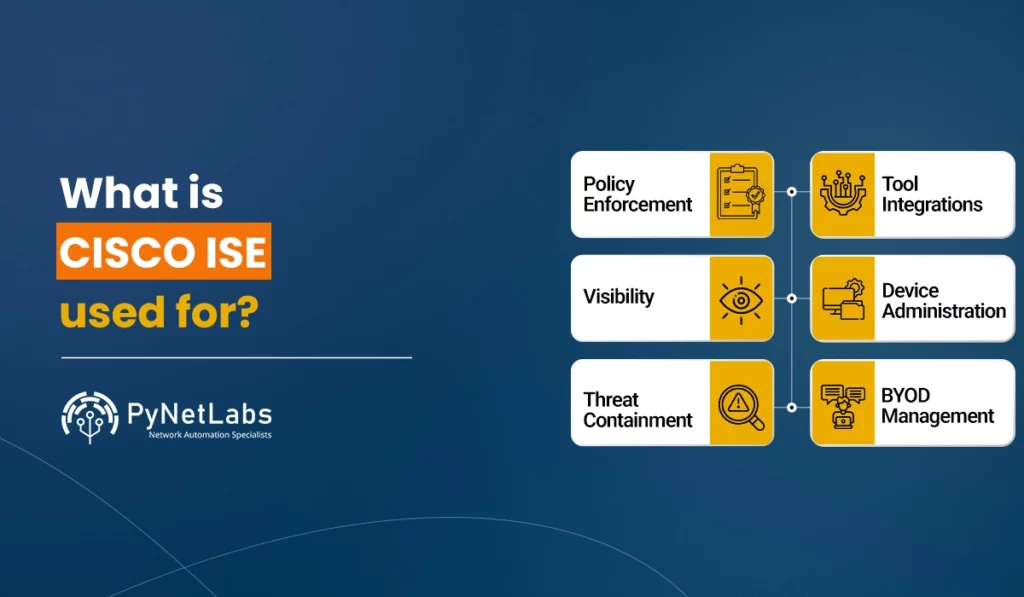

Cisco ISE is used to determine who and what devices can connect to your network, the degree of access they can be granted, and what ought to be done if a device appears suspicious. It helps companies in not treating each laptop, phone or printer, camera, guest device, as well as VPN users the same. It checks identity, device type, posture, location, and policy prior to granting access.
In this blog, we will explain Cisco ISE use cases in real business language, without making it sound more complex than needed.
What is Cisco ISE?
Cisco ISE, or Cisco Identity Services Engine is a network access control and policy platform. It assists your network in deciding whether a device or user is allowed, restricted, limited, or moved to a more secure network.
Cisco ISO Use Cases: Quick Overview
| Cisco ISE Use Case | What It Helps With |
| 1. Network access control | Decides who or what can connect |
| 2. 802.1X authentication | Verifies users and devices before access |
| 3. Guest access | Gives visitors safe internet-only access |
| 4. BYOD access | Allows personal devices with controlled policy |
| 5. Device profiling | Identifies laptops, phones, printers, IoT, and unknown devices |
| 6. IoT/OT security | Limits access for devices that cannot run agents |
| 7. Segmentation | Stops users and devices from reaching unnecessary systems |
| 8. Posture checking | Checks if devices meet security requirements |
| 9. VPN authorization | Controls remote user access based on identity and policy |
| 10. TACACS+ device admin | Controls and audits admin access to network devices |
| 11. Threat containment | Quarantines or limits risky endpoints |
How Cisco ISE Use Cases Work in Real-World Networks?
Cisco ISE use cases become easier to understand when you see how they solve everyday network access and security problems. Below, we have discussed different ways organisations use Cisco ISE across wired, wireless, VPN, guest, and device environments.
1. Cisco ISE Is Used for Network Access Control
The most common use of Cisco ISE is network access control, often called NAC. This means Cisco ISE helps decide whether a device should enter the network and what access it should receive after connecting. It works with network devices such as switches, wireless controllers, access points, and VPN gateways.
For example, when your laptop connects to office Wi-Fi, the Wi-Fi infrastructure can send an authentication request to Cisco ISE. ISE checks the user identity, device identity, certificate, group membership, or policy condition. Then it sends back the access decision.
That decision may be:
- Full employee access
- Limited contractor access
- Guest internet-only access
- Printer VLAN access
- Quarantine access
- Complete rejection
2. Cisco ISE Is Used for 802.1X Authentication
One of the strongest Cisco ISE use cases is 802.1X.
802.1X is utilized when a business needs the users or devices verify their identity prior to gaining access to the network. This is typical in Wi-Fi networks for corporate use and wired LAN environments.
Without 802.1X, devices may connect due to the fact that it is connected to the port or has the Wi-Fi password. If you use 802.1X as well as Cisco ISE the device has to authenticate correctly.
For example, an employee laptop with a valid certificate connects to the LAN. Cisco ISE verifies it and gives internal access. A personal laptop connects to the same port. ISE does not trust it and places it into a restricted network.
Benefit: Access is no longer based only on physical connection. It is based on verified identity.
3. Cisco ISE Is Used for Guest Wi-Fi Access
Guest access is one of the most practical uses of Cisco ISE.
Every company has visitors: clients, vendors, interview candidates, auditors, consultants, or temporary workers. You want them to use internet, but you do not want them inside your internal business network.
Cisco ISE helps create guest access flows such as self-registration, sponsored guest access, and hotspot access.
For example, a visitor enters their details, receives OTP or approval from a sponsor, and gets internet-only access for a fixed time. After the time expires, access stops automatically.
Benefit: Saves the IT team from manually creating and removing guest accounts every day.
4. Cisco ISE Is Used for BYOD Access
BYOD simply means Bring Your Own Device.
This is the case when employees use personal devices like tablets, phones, or laptops to get work-related access. This sound convenient however it can be risky. A personal device may not have company antivirus, patching, encryption, or management controls.
Cisco ISE helps organizations handle BYOD in a secure manner. It lets users sign up their devices for personal use as well as install certificates and have limited access in accordance with the policy.
The goal is not to completely block personal devices. It is important to allow them access that is compatible with their level of trust.
For example,
- A managed company laptop may access internal apps.
- A personal phone may access only email or internet.
- An unknown device may get no access at all.
5. Cisco ISE Is Used for Device Profiling and Visibility
One big reason companies deploy Cisco ISE is visibility. You cannot secure what you cannot see.
Many networks have unknown devices connected for years. Printers, scanners, cameras, access control systems, IP phones, smart TVs, and IoT devices often sit quietly on the network. Some of them cannot run antivirus. Some cannot use modern authentication. Some are never patched.
Cisco ISE uses profiling to understand what type of device is connecting.
For example, a printer should not have the same access as a finance laptop. A CCTV camera should not talk to HR systems. A badge reader should not browse the internet freely.
Benefit: Profiling helps convert a blind network into a visible network.
6. Cisco ISE Is Used for IoT and OT Security
IoT as well as OT device aren’t easy to secure as the majority of them weren’t created with enterprises security in mind.
Consider factory equipment such as cameras, medical devices, sensors, door control systems, and building control systems. These all are critical to business however, they do not support certificates, agents or patches that are routinely applied.
Cisco ISE is used to identify these devices, group them, and limit what they can access.
For example, a hospital can allow a medical device to talk only to required systems, not to the full corporate network. A manufacturing plant can separate production devices from employee laptops.
Benefit: Reduces the damage if one weak device is compromised.
7. Cisco ISE Is Used for Network Segmentation
Cisco ISE is not only about allowing or blocking access. It is also used to control movement inside the network.
It can assign Security Group Tags, or SGTs, to users and devices according to their role or classification. Network policy can then control communication between those groups.
A practical example:
- HR users can access HR applications.
- Finance users can access finance systems.
- Printers can access print servers only.
- Guests can access internet only.
- IoT devices can access only their controllers.
This is where Cisco ISE becomes more than a login tool. It becomes a policy engine for the network.
8. Cisco ISE Is Used for Posture and Compliance Checks
Another important Cisco ISE use case is posture checking. Posture is the process of determining if the device is in good health before granting access.
For example, Cisco ISE can help to determine whether a device comes with the required security tools including patches, antivirus, disk encryption, or other compliance criteria. This is especially useful in areas where compliance is a concern like healthcare, banking, government, as well as large companies and other industries that are regulated.
The access decision can change based on posture.
- A compliant laptop gets normal access.
- A non-compliant laptop gets remediation access.
- A risky device is quarantined or blocked.
Benefit: Makes security more active, not just checklist-based.
9. Cisco ISE Is Used for VPN Access Control
Cisco ISE is also used for remote access control.
If users connect using VPN, the same question still matters : who’s connecting, what device is it and what can they access?
ISE can be integrated with VPN infrastructure by using RADIUS-based authenticating and authorizing. This lets companies apply rules for remote users, not only office users.
For example:
- An employee who is full-time and has managed laptops may have access to internal software.
- A contractor who uses VPN might only have access to a specific project server.
- Anyone who has a risky device could be denied or have limited access.
Benefit: keeps access consistent whether the person is inside the office or working remotely.
10. Cisco ISE Is Used for Network Device Administration
Cisco ISE is also used to control admin access to network devices.
This is different from user access to the network. Here, the question is: which engineer can log in to routers, switches, wireless controllers, or firewalls, and what commands can they run?
Cisco ISE supports TACACS+ for device administration.
This matters because not every network engineer should have full admin access everywhere.
For example:
- A junior engineer may get read-only access.
- A senior engineer may change switch configuration.
- A security admin may manage firewall-related settings.
- Every command can be logged for audit.
Benefit: Helps with accountability and reduces the risk of accidental or unauthorized changes.
11. Cisco ISE Is Used for Threat Containment
Cisco ISE can also help respond when a device becomes risky after it has already connected.
This is important because trust should not be permanent. A device may be safe in the morning and risky by afternoon if it gets infected or starts behaving strangely.
Cisco ISE is able to integrate with Cisco and other security tools from third parties through pxGrid as well as other integrations.
For example, If an antivirus tool finds an infected laptop, Cisco ISE can help to change the network access of the laptop. The device could be transferred into quarantine or be given limited access until the issue is addressed.
Benefit: Connects detection with enforcement.
Frequently Asked Questions
Q1. What is the purpose of ISE?
Cisco ISE controls who and what can access a network and applies the correct access rules.
Q2. What is replacing Cisco ISE?
Nothing officially replaces Cisco ISE; Cisco still develops it. Other NAC platforms are alternatives, not its official successor.
Q3. Is Cisco ISE difficult to learn?
It can feel difficult initially, but understanding networking, RADIUS, and 802.1X makes learning much easier.
Q4. Is Cisco ISE a SIEM tool?
No. Cisco ISE controls network access, while a SIEM collects and analyses security logs and alerts.
Conclusion
So, What is Cisco ISE used for? It helps make sure that network access is controlled. It assists in moving away from a simple and trust-based network in which every connected device has too much access. Instead, it allows you to create a system where access is based on the identity of the device, its type, health, the role, location, as well as the risk.