
Cisco ISE Architecture is built around the specialised nodes and network access devices, endpoints, identity sources and security integrations that work together to control and monitor the access to networks. Instead of allowing a device to connect simply because it has reached a switch or wireless network. Cisco identity services engine checks the user, device connection method, security posture and applicable policy before granting access to the device.
This architecture can be deployed on a single node for a limited environment or distributed across several nodes for better performance, scalability, and availability. Understanding how these components communicate is important for anyone working with network access control, Cisco security, or the Cisco ISE platform.
Key Takeaways
✔ Cisco ISE is a centralized Network Access Control (NAC) solution.
✔ The four core personas are PAN, PSN, MnT, and pxGrid.
✔ Network devices enforce policies while PSNs make access decisions.
✔ Cisco ISE supports standalone, distributed, and high-availability deployments.
✔ It integrates with Active Directory, LDAP, Certificates, and security platforms.
What Is Cisco ISE Architecture?
Cisco ISE Architecture describes how Cisco Identity Services Engine nodes, network devices, endpoints, identity stores, and security platforms are organised to provide identity-based access control.
Cisco ISE operates as a central policy platform. It receives access requests from infrastructure devices such as switches, wireless LAN controllers, routers, and VPN gateways. It then evaluates the request using information such as:
- User identity
- Device type
- Network location
- Authentication method
- Security posture
- Active Directory group
- Time and connection conditions
Main Building Blocks of Cisco ISE Architecture
Cisco ISE architecture can be understood through three broad component groups:
| Component | What It Includes | Main Responsibility |
| Infrastructure components | Switches, wireless controllers, routers, VPN gateways and firewalls | Receive connections and enforce ISE decisions |
| Policy components | ISE policies, identity rules, authorization rules and profiling conditions | Decide what level of access should be provided |
| Endpoint components | Laptops, phones, printers, IP phones and IoT devices | Request access to the network |
1. Infrastructure Components
Infrastructure components are the devices that connect endpoints to the network. Common examples include:
- Access switches
- Wireless LAN controllers
- Wireless access points
- Routers
- VPN concentrators
- Firewalls
- Private 5G infrastructure
These devices are commonly called network access devices, or NADs. A switch or router configured as an authentication, authorization, and accounting (AAA) client sends access requests to Cisco ISE.
The network access device does not normally make the complete identity-based decision by itself. It collects information from the endpoint, sends the request to an ISE Policy Service Node, and applies the response it receives.
The response may allow normal access, reject the connection, assign a VLAN, apply a downloadable access control list, redirect the user to a portal, or assign a Security Group Tag.
2. Policy Components
Policy components define the conditions under which users and devices can access the network.
Cisco ISE policies usually include:
- Policy sets
- Authentication policies
- Authorization policies
- Authorization profiles
- Identity source sequences
- Profiling policies
- Posture policies
- Guest access rules
For example, an authorization policy may state that a corporate Windows laptop used by a finance employee can access finance applications. A personal mobile phone belonging to the same employee may receive only internet access.
3. Endpoint Components
Endpoints are the devices or identities requesting access. These may include:
- Employee laptops
- Personal mobile phones
- Corporate tablets
- Printers
- IP phones
- Cameras
- Medical devices
- Industrial systems
- IoT sensors
Endpoints may authenticate through 802.1X, MAC Authentication Bypass, web authentication, or another supported access method. Endpoint information may also be collected through profiling probes and posture assessment.
Cisco ISE Architecture Flow
| Stage | Component | What Happens |
| 1 | User or endpoint | A laptop, phone, printer, or IoT device requests network access. |
| 2 | Network access device | A switch, wireless controller, VPN gateway, or firewall receives the connection request. |
| 3 | Policy Service Node | The PSN processes the authentication request and evaluates the relevant access policies. |
| 4 | Identity source | Cisco ISE verifies the user or device through Active Directory, LDAP, certificates, or its internal database. |
| 5 | Authorization decision | Cisco ISE decides whether to allow, restrict, redirect, or deny access. |
| 6 | Policy enforcement | The network device applies the result received from Cisco ISE. |
| 7 | Monitoring | The MnT node records authentication details, logs, alarms, and reports. |
| 8 | Security integration | pxGrid shares identity and endpoint context with connected security tools. |
This flow explains how Cisco ISE acts as the central policy decision platform while switches, wireless controllers, firewalls, and VPN gateways enforce its access decisions.
Core Cisco ISE Personas
A persona is the role assigned to a Cisco ISE node. Cisco ISE 3.5 identifies four main personas: Administration, Policy Service, Monitoring, and pxGrid.
1. Policy Administration Node
A node running the Administration persona is commonly called a Policy Administration Node, or PAN.
The PAN provides the central management interface for the ISE deployment. Administrators use it to configure:
- Network devices
- Authentication policies
- Authorization rules
- Identity sources
- Certificates
- Guest services
- Profiling rules
- Node settings
- Administrative access
2. Policy Service Node
The Policy Service Node, or PSN, is the real-time decision engine in Cisco ISE Architecture.
When a switch, wireless controller, or VPN gateway receives a connection request, it forwards the relevant AAA request to a PSN. The PSN then:
- Identifies the network device sending the request.
- Determines which policy set should process it.
- Selects the permitted authentication protocol.
- Checks the identity against the configured identity source.
- Evaluates authorization conditions.
- Returns an access decision to the network device.
Want to see how Policy Service Nodes, authentication, authorization, and policy configuration work in a real environment? Explore the PyNet Labs Cisco ISE Training Course and gain hands-on experience through live instructor-led labs.
3. Monitoring and Troubleshooting Node
The Monitoring persona runs on the Monitoring and Troubleshooting Node, commonly shortened to MnT.
Its responsibility is to collect, store, correlate, and present operational information from the deployment. This includes:
- Authentication records
- Authorization results
- RADIUS accounting data
- Administrative audit logs
- System alarms
- Endpoint information
- Troubleshooting reports
4. pxGrid Node
Cisco Platform Exchange Grid, or pxGrid, allows Cisco ISE to exchange identity and network context with other security systems.
Through pxGrid, ISE can share information such as:
- User identity
- Endpoint identity
- IP address
- Security Group Tag
- Authentication status
- Device profile
- Session information
- Network location
How a Network Access Request Moves Through Cisco ISE
A basic Cisco ISE authentication flow works as follows:
Step 1: An Endpoint Connects
A user connects a laptop to a switch port, joins a wireless network, or establishes a VPN connection.
Step 2: The Network Device Starts Authentication
The switch, wireless controller, or VPN gateway collects the endpoint’s authentication information. The network device acts as the AAA client.
Step 3: The Request Reaches a PSN
The network device sends a RADIUS or TACACS+ request to the configured Policy Service Node. Cisco documents the PSN as the main engine for processing network access requests and applying security policies.
Step 4: Identity Is Verified
The PSN checks the identity against an available source. This may be Microsoft Active Directory, LDAP, an internal ISE identity store, a certificate authority, or another configured source.
Step 5: Authorization Policy Is Evaluated
ISE considers the available context, including identity group, device profile, authentication method, network location, posture status, and other conditions.
Step 6: An Authorization Result Is Returned
The PSN returns an access decision. The network device then enforces that result by permitting, rejecting, limiting, segmenting, or redirecting the connection.
Step 7: Logs Are Sent to MnT
Authentication and accounting information is collected by the Monitoring node for reporting, audits, and troubleshooting.
Step 8: Context May Be Shared Through pxGrid
Relevant session and endpoint information can be shared with connected security systems.
Cisco ISE Deployment Models
The arrangement of personas depends on the size, availability, and performance requirements of the environment.
Standalone Deployment
A standalone deployment contains one Cisco ISE node running the Administration, Policy Service, and Monitoring personas.
It is relatively simple, but the same node must manage configuration, process authentication requests, and collect logs. Cisco defines any deployment containing only one ISE node as standalone.
Standalone deployment is generally more suitable for laboratories, testing, demonstrations, and limited environments where high availability is not required.
Two-Node or Small Deployment
A small production design can use two ISE nodes, with one operating as the primary and the second providing backup capability.
Cisco’s small-network guidance describes a two-node design in which configuration is synchronised and both nodes can be configured on RADIUS clients. If the primary path becomes unavailable, the secondary node can continue supporting network operations.
Split Deployment
In a split deployment, management and monitoring functions are separated from policy processing.
For example:
- Two nodes may run Administration and Monitoring personas.
- Separate nodes may run the Policy Service persona.
This prevents authentication traffic from competing directly with management and reporting workloads.
Distributed Deployment
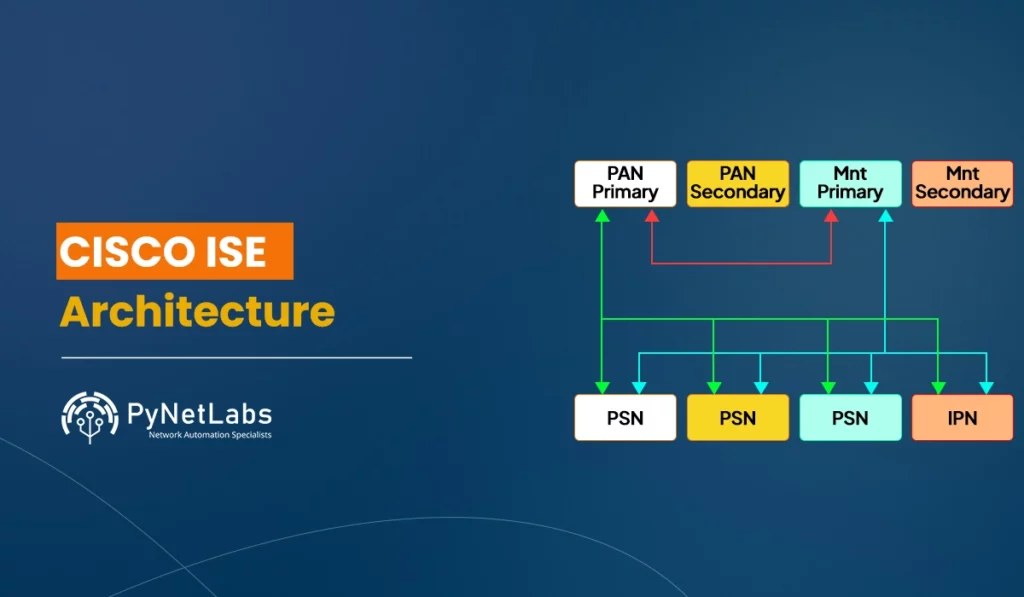
A distributed Cisco ISE Architecture uses dedicated nodes for different functions. A typical design may include:
- Primary and secondary PANs
- Primary and secondary MnT nodes
- Multiple PSNs
- One or more pxGrid nodes
Cisco describes distributed deployment as a model in which administration and monitoring remain centralised while authentication and policy processing are distributed across PSNs.
For medium-sized deployments, Cisco requires dedicated Policy Service nodes rather than enabling the Policy Service persona on nodes running Administration or Monitoring personas.
Important Design Considerations
A good Cisco ISE design should not be based only on the number of users. You should also consider:
- Peak authentication requests
- Number and type of endpoints
- Geographic locations
- WAN reliability
- Guest and BYOD services
- Profiling traffic
- Posture assessment
- Log volume
- Device administration traffic
- Security integrations
- Recovery requirements
Place PSNs close enough to network access devices to maintain reliable authentication. Use redundant PSNs for important locations and configure network devices with alternative RADIUS servers.
Administration and Monitoring nodes should also have high availability where access control is business-critical. Certificates, DNS, NTP, firewalls, identity sources, and required network ports must be included in the architecture plan because an ISE node cannot operate correctly when these supporting services are unreliable.
Conclusion
Cisco ISE Architecture separates network access into clear functional areas. Endpoints request access, network devices forward and enforce requests, PSNs make real-time decisions, PANs manage configuration, MnT nodes store operational data, and pxGrid connects ISE with the wider security ecosystem.
A small environment may combine these functions on one or two nodes. As authentication volume and business requirements grow, a distributed design provides better performance, fault isolation, scalability, and operational visibility.
The most important point is that Cisco ISE is not simply a RADIUS server. Its architecture creates an identity-aware policy system that can identify users and devices, evaluate their context, control what they can access, and share that information with other security technologies.
FAQs About CISCO ISE Architecture
Q1. What are the main components of Cisco ISE Architecture?
Ans. The main components are PAN, PSN, MnT, pxGrid, network devices, endpoints, identity sources, and integrated security tools.
Q2. What is the role of a Policy Service Node?
Ans. A Policy Service Node authenticates users and devices, evaluates authorization policies, and returns access decisions to network equipment.
Q3. How is standalone Cisco ISE different from distributed deployment?
Ans. Standalone deployment combines personas on one node, while distributed deployment separates roles across multiple nodes for scalability and resilience.
Q4. What does pxGrid do in Cisco ISE Architecture?
Ans. pxGrid shares identity, device, session, and security context between Cisco ISE and compatible security platforms or applications.